

Blog
Insights on compliance automation.
Guides and articles on automating evidence collection, generating policies from real infrastructure, and getting audit-ready across SOC 2, HIPAA, and ISO 27001.
10 Compliance Automation Trends That Actually Changed in 2025 and Will Matter in 2026
Compliance automation shifted from simple infrastructure monitoring to AI-agentic evidence capture in 2025. Discover the ten trends, including the closure of the '20% manual gap' and automated CMMC 2.0 readiness, that will define the audit landscape in 2026.
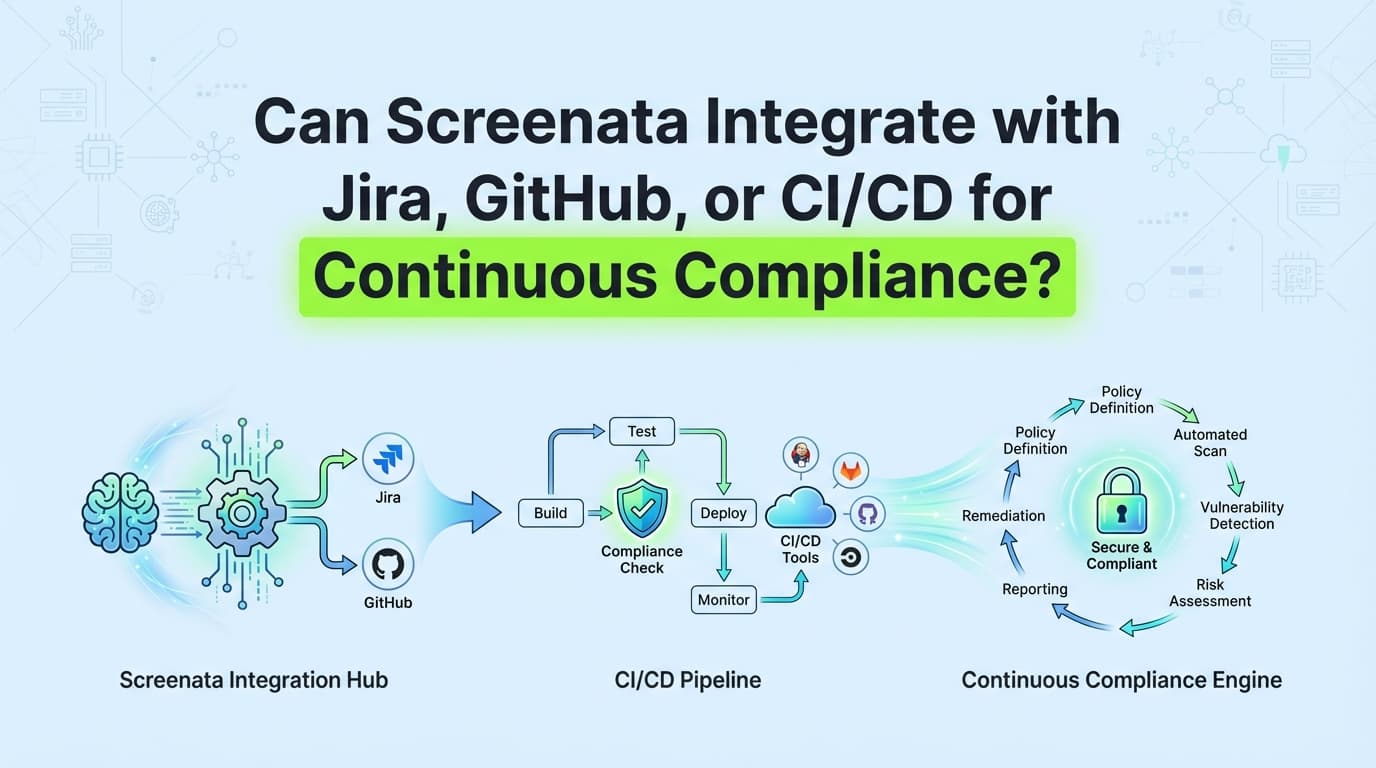
Can Screenata Integrate with Jira, GitHub, or CI/CD for Continuous Compliance?
Screenata integrates with Jira, GitHub, and CI/CD pipelines to enable continuous compliance by triggering AI-driven evidence collection during the development lifecycle. This integration automates documentation for change management (CC7.2) and access controls (CC6.1), ensuring audit-ready evidence is captured at the moment of action.
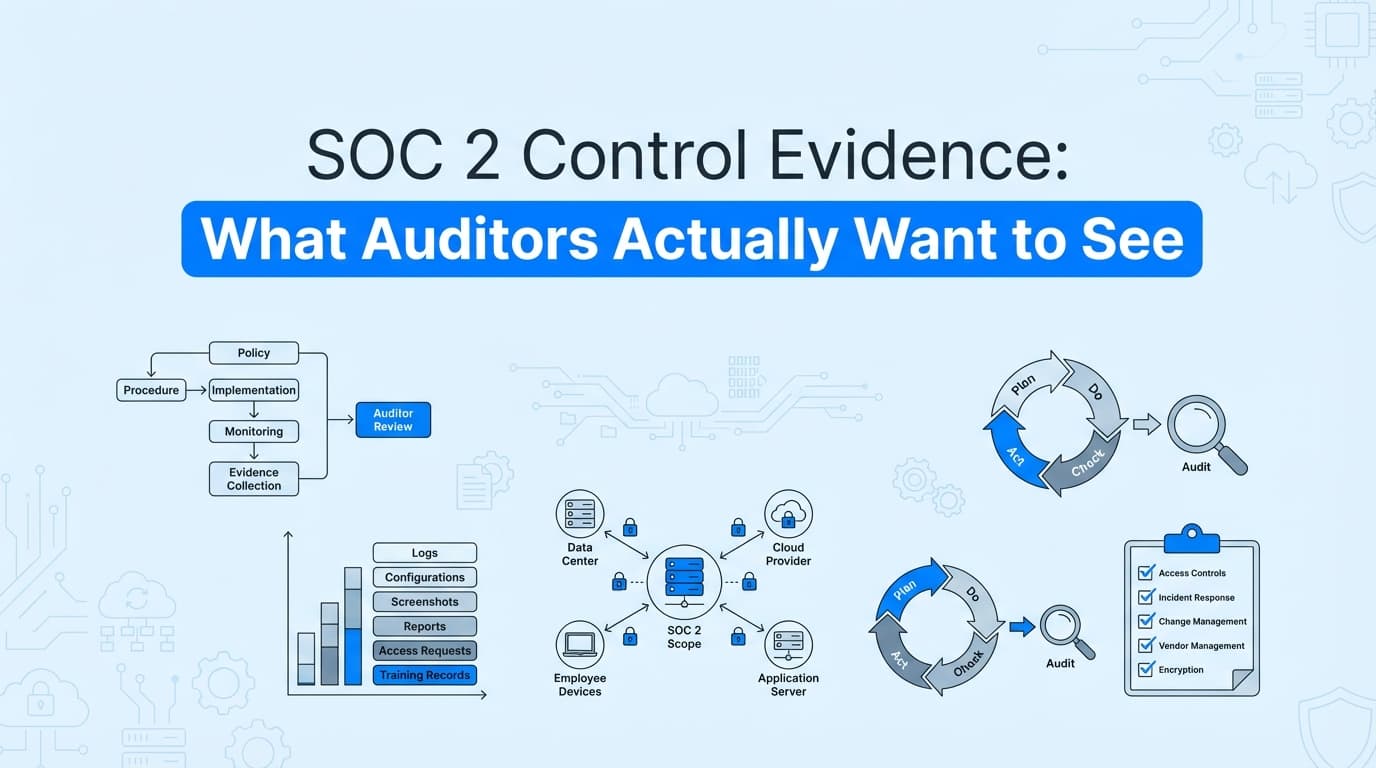
What SOC 2 Evidence Do Auditors Require for Application Controls?
SOC 2 application evidence links each control to its system, date, owner, and operating records. See access and change-management examples, plus completeness checks.
How to Collect SOC 2 CC8 Evidence When Changes Are Manual with Screenshots
Yes. AI tools can automatically capture SOC 2 CC8 evidence for manual changes by recording workflows, validating screenshots, and generating audit-ready reports. This article explains how to satisfy change management requirements for SaaS configurations and manual processes where traditional GRC automation fails.
What Auditors Still Ask for After Drata Automation: Missing SOC 2 Evidence
Drata automates infrastructure over API, then marks the application controls manual and waits. This guide shows what auditors still ask for after Drata (application RBAC proof, change approvals, access reviews) and how Vera, an agent who runs continuous compliance, does that work: capturing UI proof for CC6.1 and CC7.2, chasing the attestations only a person can answer, and filing signed, traceable packs that sync back to Drata.
HITRUST CSF vs SOC 2: Evidence Requirements Compared
HITRUST r2 assessments demand significantly more rigorous evidence than SOC 2, requiring documentation across five maturity levels. This guide compares the specific evidence requirements for both frameworks and explains how to automate collection for MyCSF and audit partners.
How to Achieve 100% SOC 2 Automation with Vanta and Screenshot Tools
Vanta monitors your infrastructure and leaves the rest to you, which means 40 to 60 hours of evidence chasing per audit. Screenata closes that gap with an agent named Vera who runs the program, collecting infrastructure and application evidence, chasing attestations in Slack, and tracing every artifact back to a control. This guide shows how to reach full coverage, whether you keep Vanta or replace it.
What Makes SOC 2 Evidence Acceptable to Auditors? Quality Checklist
SOC 2 auditors require screenshots with timestamps, metadata, tester identity, and control mapping, not just static images. This checklist shows what makes SOC 2 evidence acceptable for application controls like CC6.1 and CC7.2, including AICPA standards for sufficiency, reliability, and relevance.
How Continuous Compliance Automation Reduces Risk of SOC 2 Audit Failure
Continuous compliance automation eliminates the risk of audit failure by replacing last-minute manual screenshots with always-on evidence capture. This article explains how AI tools automate SOC 2 evidence collection to prevent control drift and missing documentation.
How Drata Works for SOC 2: Architecture, Integrations, and Limits
Drata connects to 75+ integrations via read-only APIs to monitor your infrastructure. This guide explains how Drata's architecture works, which integrations matter most for SOC 2, where the monitoring model hits its limits with application controls and attestations, and how Vera, an agent that runs continuous compliance, does the work a dashboard only flags.
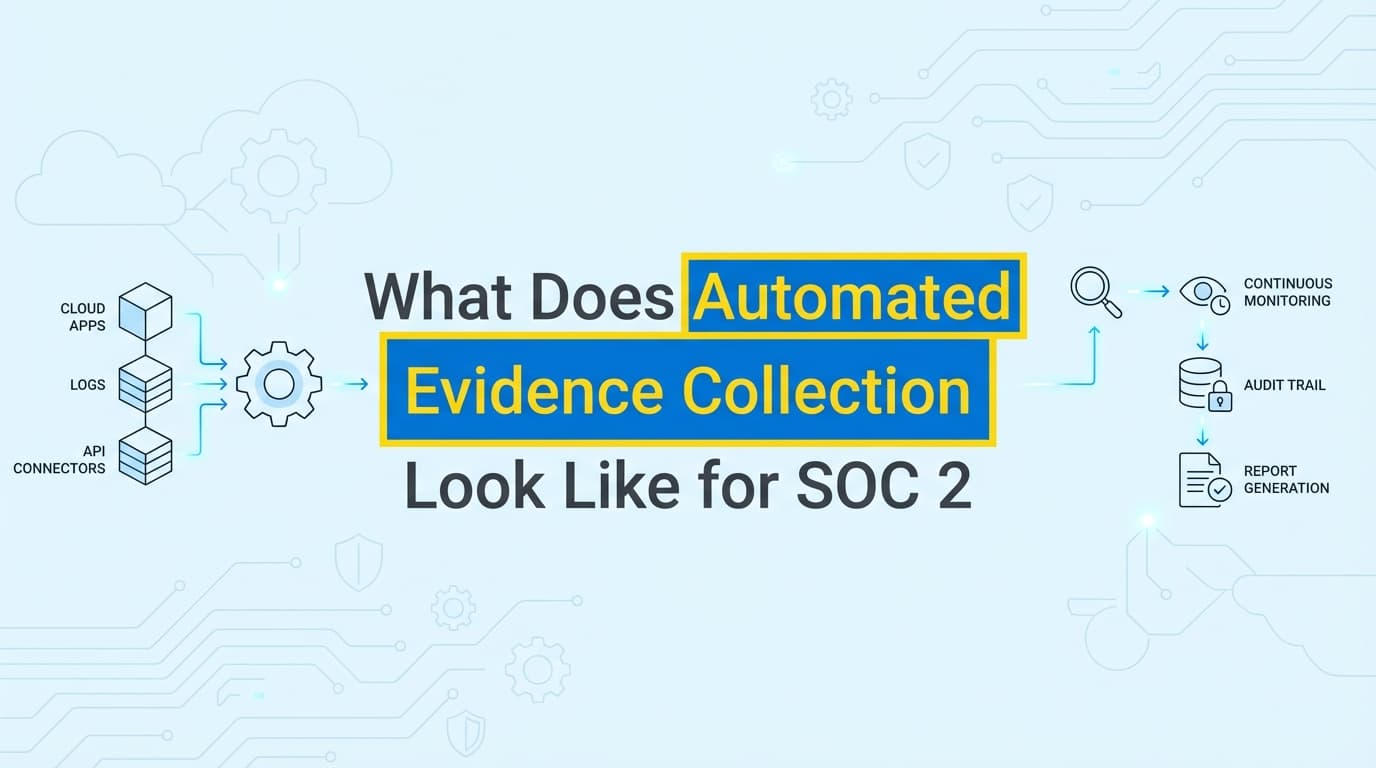
What Does Automated Evidence Collection Look Like for SOC 2
Automated SOC 2 evidence collection is an agent that captures application tests, screenshots, and metadata, then signs and files them. Screenata's agent Vera runs the test, scores the capture, chases the attestations only a person can answer, and files signed packs that close the 20% gap a dashboard leaves open.
How to Automate SOC 2 Evidence Collection with Screenshots in 2025
To automate SOC 2 evidence collection, use GRC platforms (Drata, Vanta) for infrastructure APIs (80%) plus screenshot automation for application evidence (20%). This guide shows step-by-step how to automate SOC 2 screenshots, workflow documentation, and audit-ready reports, reducing manual work from 80 hours to 6 hours per audit.