

Blog
Insights on compliance automation.
Guides and articles on automating evidence collection, generating policies from real infrastructure, and getting audit-ready across SOC 2, HIPAA, and ISO 27001.
How Much Time Does SOC 2 Audit Preparation Actually Take? (Hours vs. Months)
SOC 2 prep typically spans 3-6 months for Type 1 and 6-12 months for Type 2, but the actual labor hours vary significantly based on tooling. This guide breaks down the engineering time required for remediation, policy work, and manual evidence collection.
What Counts as Enough SOC 2 Evidence? Screenshots, Exports, and Review Records
Worked examples of SOC 2 evidence using exports, logs, screenshots, reviewer sign-off, and remediation records. Learn how to clarify evidence expectations with your auditor and preserve complete populations without relying on universal screenshot or sampling rules.
AI Agents vs. API Integrations: The New Stack for SOC 2 Evidence
Compliance automation has evolved beyond simple API connections. While APIs handle infrastructure monitoring, AI agents now capture the application-level screenshots required for SOC 2 evidence. This guide compares the two technologies and explains how to build a hybrid stack for complete audit automation.
The vCISO’s Guide to Automating Audit Prep Across Portfolios
Managing compliance for multiple clients breaks down when you hit the evidence collection phase. This guide explains how vCISOs automate manual screenshots and audit prep to protect margins and scale their practice.
How MSPs Automate Compliance Evidence Collection for Multiple Clients
MSPs often struggle to scale compliance services due to the manual labor of collecting evidence. This article explains how to automate evidence collection for SOC 2 and HIPAA across multiple clients using AI agents, reducing the need for linear headcount growth.
Automating CMMC Level 2 Evidence Collection: What APIs Can't Capture
CMMC Level 2 assessments require objective evidence that goes beyond API-based configuration checks. This article explains why C3PAO assessors demand screenshots for application-level controls and how to automate CMMC level 2 evidence collection for hybrid environments.
How to Capture HIPAA Evidence for EHR Access Logs and Admin Panels
HIPAA audits require more than just raw log data; they demand proof that your logging configuration is active, tamper-proof, and retaining data correctly. This guide explains the specific screenshots and evidence artifacts auditors need for EHR access logs and how to automate their collection.
How to Bridge the Drata Automation Gap for SOC 2 Evidence
Drata automates infrastructure compliance via APIs, but application-layer evidence and periodic attestations stay manual. This guide explains how Vera, an agent that runs continuous compliance, does the work a dashboard only flags: capturing application evidence, chasing sign-offs, and filing signed, traceable packs, alongside Drata or in place of it.
SOC 2 Type 2 Quarterly Evidence Checklist: What to Collect and When
Use a quarterly checkpoint to keep SOC 2 Type II evidence current, with named owners, review decisions, remediation links, and checks for control drift. Match collection to your approved control cadence and agree testing expectations with your auditor.
How to Audit SaaS Vendor Access Controls and Incident Response
Auditing SaaS vendor security requires more than collecting a SOC 2 report. This guide explains how to verify specific access control and incident response evidence within vendor documentation to satisfy SOC 2 CC9.2 and ISO 27001 A.5.19 requirements.
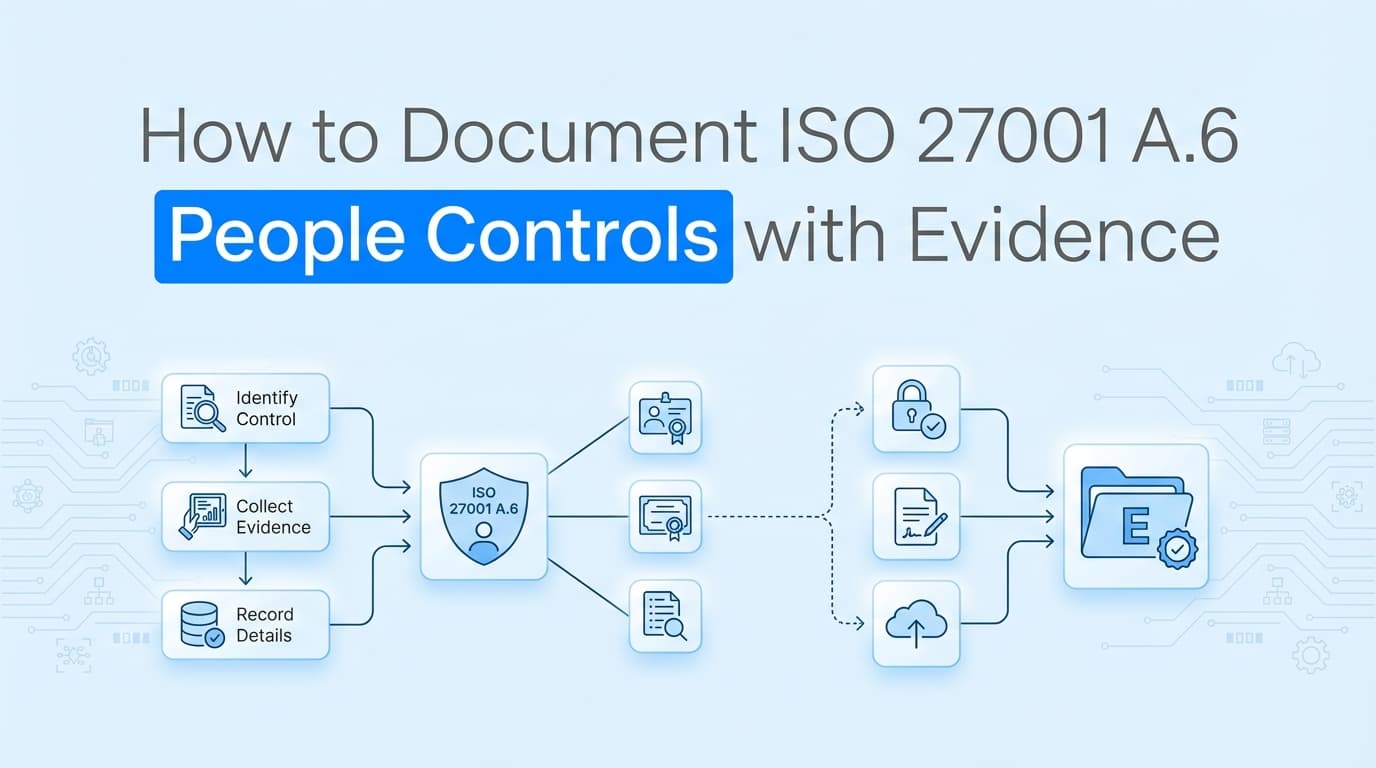
How to Document ISO 27001 A.6 People Controls with Evidence
ISO 27001 A.6 controls require specific evidence for screening, training, and offboarding. This guide explains exactly what documents auditors accept for People Controls and how to automate evidence collection without exposing sensitive HR data.
SOC 2 Evidence Preparation Checklist: How to Automate Screenshots Before an Audit
SOC 2 evidence prep fails on the artifacts, not the policies. This checklist covers what auditors request domain by domain, from CC6 access controls to CC8 change management, and shows how Vera collects most of it through scans, captures the application-level screenshots APIs cannot reach, and chases the attestations only a person can answer.